This is exactly where the combination of adesso’s consulting expertise and OneTrust’s tool support comes into play. The sequence is intentionally as follows:
adesso works with its clients to develop the appropriate TPRM roadmap, embeds it within the organization, and translates regulations into practical governance. OneTrust then provides the platform on which this governance is implemented in a scalable, automated, and traceable manner.
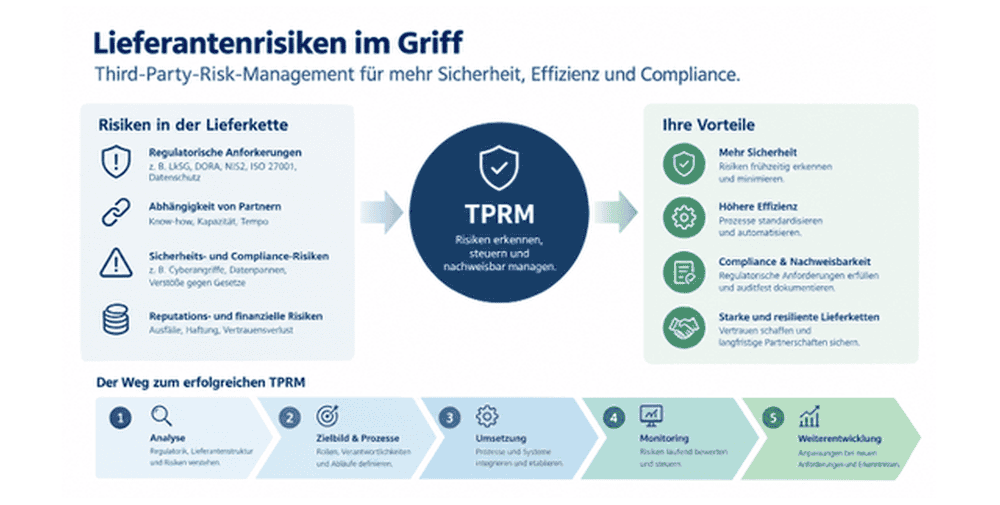
Many companies already have elements of third-party risk management in place: questionnaires, security audits, compliance checks, and individual LkSG or data protection processes. However, what is often missing is the overarching framework that brings everything together: a comprehensive understanding of TPRM that connects regulation, risk appetite, procurement, IT, compliance, information security, and business units.
This is exactly where adesso comes in. First, regulatory and strategic frameworks are organized: Which laws, norms, and standards apply; which parts of the supplier landscape are affected; and how do the LkSG, DORA, NIS2, ISO 27001, and data protection laws specifically impact operations? This provides a clear picture of obligations and their impact on processes and data.
Building on this, adesso develops a TPRM target model grounded in practical experience. First, roles and responsibilities are defined. Next, adesso describes the entire process, from the initial request for requirements to contract termination. In addition, it specifies how risks are assessed and managed. Risk models, questionnaires, criteria for critical suppliers, and catalogs of measures are derived from best practices and tailored to the organization.
This target model is consistently implemented in day-to-day operations. adesso embeds processes in procurement, business units, IT, and risk functions; integrates existing GRC, ICS, and ISMS structures; and supports the change process with training and coaching. Insights from initial assessments are directly incorporated into the further development of criteria, workflows, and governance rules.
OneTrust as an Enabler—and adesso as the Architect Behind the Scenes
OneTrust can deliver its full value on the foundation developed by adesso. Without a governance design, a tool often remains limited to digitizing existing Excel spreadsheets. With clear governance, it becomes an enabler of transparency and automation.
adesso translates the developed process and role model into the OneTrust configuration. The supplier structure and risk categories are reflected in the inventory, while questionnaires and workflows map out the end-to-end process from data collection through assessment to monitoring. Regulatory requirements are translated into specific content and logic, ensuring that all requirements are systematically addressed within the TPRM.
At the same time, adesso integrates OneTrust into the existing IT landscape.
Internal systems and external sources can be connected.
This creates a shared database on which TPRM decisions are made.
Technology follows governance, not the other way around.
Typical Project Flow: From Assessment to Ongoing Program
A TPRM project with adesso and OneTrust begins with an assessment. Processes, roles, tools, and existing documentation are analyzed, and relevant regulatory requirements are mapped to the business model. This provides a picture of the current state and key gaps.
In the next step, a TPRM target state is developed and specified in a blueprint phase: Standard processes, a risk model, questionnaires, and measures are defined, and roles and information flows are clearly described. An implementation blueprint specifies which functions will be mapped in OneTrust and which will remain in other systems.
This is followed by configuration, integration, and the setup of dashboards and audit trails. In a pilot phase with selected suppliers, processes and settings are tested and adjusted under real-world conditions before a phased rollout begins. During ongoing operations, the TPRM system is further developed based on regulatory changes, key metrics, and experience, and is regularly aligned with the business model and risk appetite.
Efficiency, Transparency, and Audit Readiness as Outcomes
The combined approach of adesso and OneTrust aims to achieve greater efficiency and better governance. Through deliberate process design and subsequent digitization, a seamless workflow is created instead of a patchwork of tools. Procurement, business units, risk, compliance, and IT operate according to clear steps and responsibilities, and tasks that can be standardized are automated.
A unified risk model and clear criteria provide a consistent view of supplier risks. Dashboards and reports follow a logic derived from governance and provide a reliable basis for decision-making. At the same time, audit readiness increases: histories, audit logs, decisions, and measures are documented in a traceable manner, and regulatory requirements from the LkSG, DORA, and NIS2, as well as those related to information security and data protection, can be transparently demonstrated.
Third-Party Risk Management as a Strategic Governance Project
Third-Party Risk Management is more than just introducing a new tool or sending out questionnaires. At its core, it is a governance project that requires a robust design, clear processes, and a culture of accountability that is actively practiced. This is precisely where adesso comes in: Regulatory requirements are translated into practical structures, roles and processes are designed to function effectively in day-to-day operations, and the organization is actively supported throughout this journey.
In this setup, OneTrust assumes the role of technical enabler. The platform ensures that governance isn’t just confined to policies, but is made visible through automated workflows, structured data, consistent assessments, and meaningful reports. Together, these elements transform a single project on supplier risks into a strategic third-party risk management program that makes organizations more resilient, boosts operational efficiency, and enhances regulatory compliance.
– – – – –
Related Links
👉 www.adesso.de
Graphic: adesso